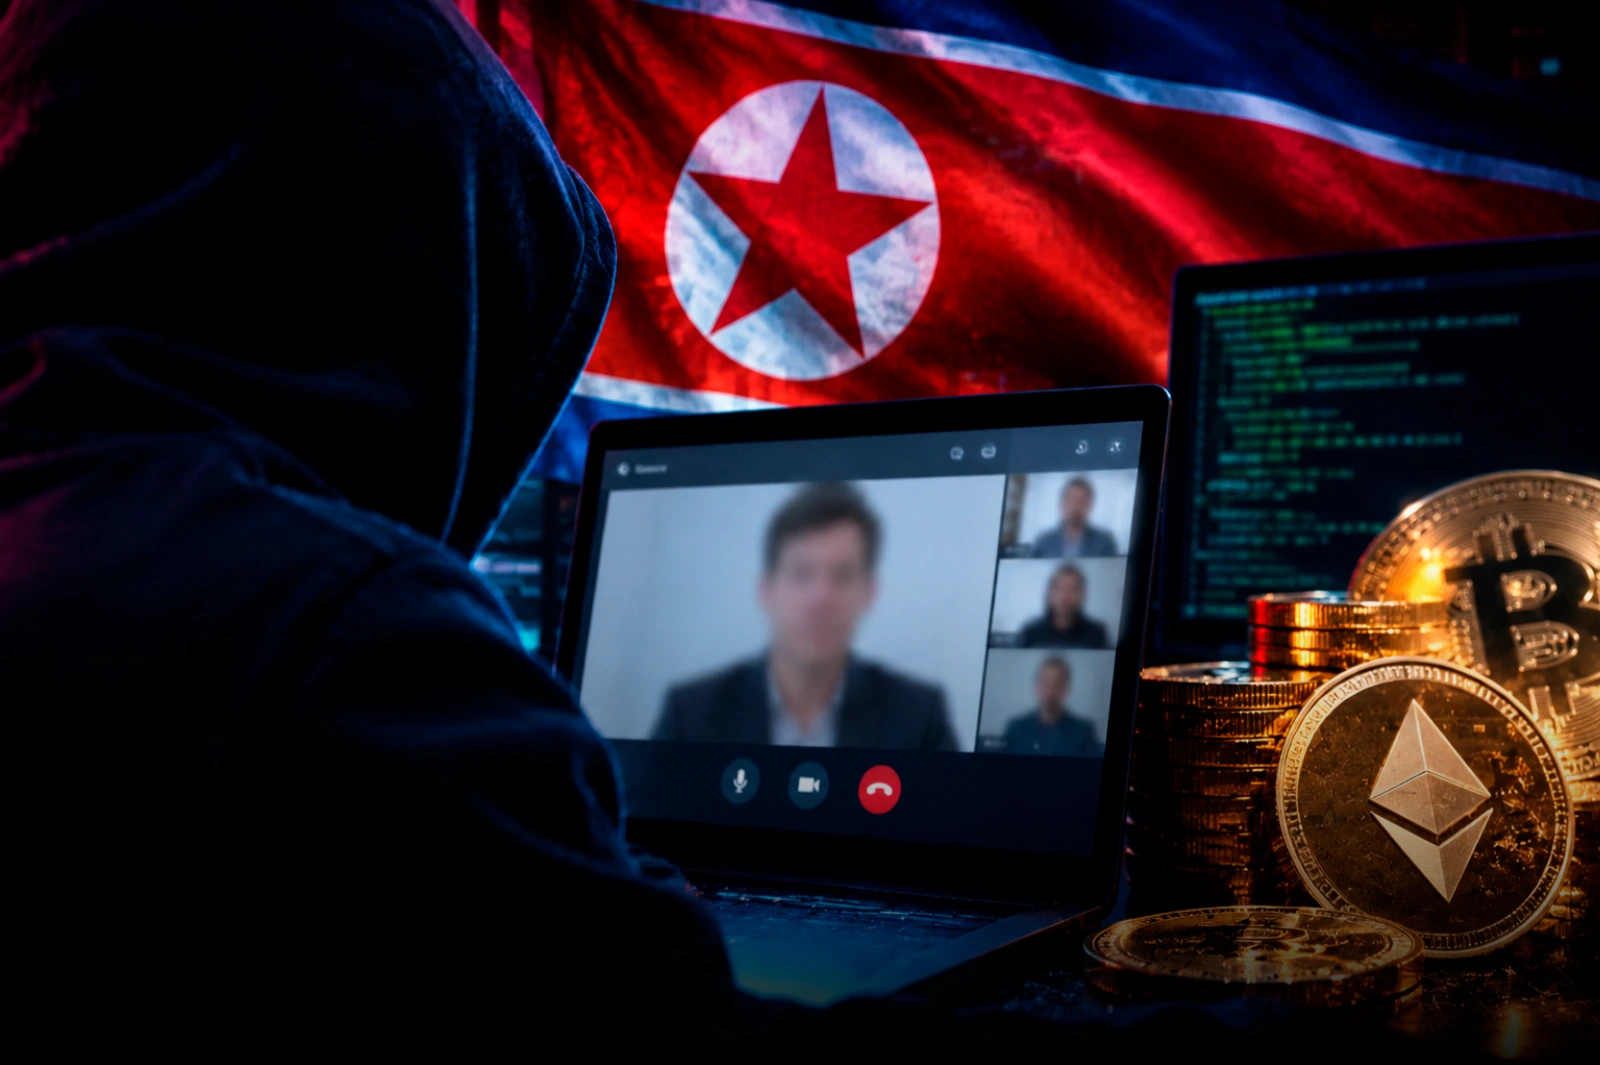
Hackers linked to the regime of North Korea stole more than 400 million dollars in cryptocurrencies through a sophisticated identity theft campaign that uses fake video calls to infect devices and access confidential information. The FBI identified the operation as ''FaceStealer'' and warned that more than 900 people have fallen victim to the scheme over the past 18 months.
The investigation by U.S. authorities indicates that the attackers use fake or hijacked social media accounts to contact potential victims and invite them to participate in virtual meetings. The campaign particularly targets workers in the cryptocurrency and ''Web3'' sectors, including developers and specialists responsible for maintaining open-source programs.
According to the FBI and the U.S. Department of Justice, the criminals organize video calls using fraudulent versions of widely used platforms, such as Zoom, Microsoft Teams, and Google Meet. In this way, they seek to build trust and make their targets believe they are participating in a legitimate meeting with acquaintances or professional contacts.
During the calls, the attackers play previously recorded videos of other victims that the contacted person recognizes. The goal is to simulate an authentic conversation, although a supposed technical problem with the audio later appears.
At that moment, a notification on the screen asks the user to resolve the issue by clicking on a link. However, the supposed repair mechanism installs malicious software on the device.
Once executed, the malware allows hackers to access the contact lists and various applications on the compromised device. This provides them with information to expand the operation and select new targets, leveraging the personal and professional relationships of the initial victims.