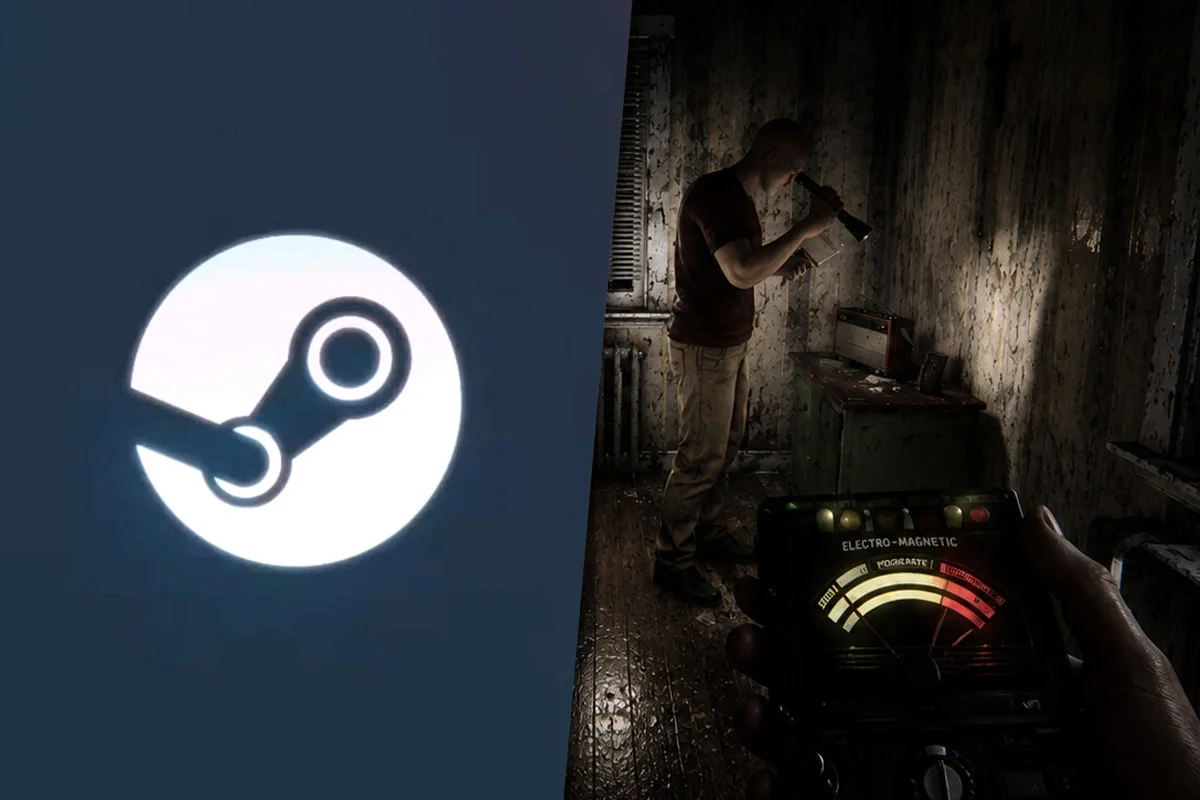


Valve removed the free game Beyond The Dark from Steam after a technical investigation revealed it contained malware capable of stealing user information.
The case gained relevance after an analysis published by specialized YouTuber Eric Parker, who detected suspicious activity within the files of the supposed horror game developed in Unity.
What was discovered inside Beyond The Dark
According to the investigation, the game hid malicious code within the UnityPlayer.dll file. The malware ran in the background while the game functioned normally as a facade.
Eric Parker explained that the software was capable of communicating with external servers and downloading additional malware components.
How the malware detected on Steam worked
The technical analysis was conducted within an isolated virtual machine to avoid compromising real systems. Although initially Windows Defender did not detect threats, specialized tools like Procmon allowed for the identification of abnormal network activity.
The investigator also discovered that the game loaded the Unity engine reflectively while executing hidden processes.
What data the malware sought to steal
According to Eric Parker's video, the malware had functions aimed at stealing information related to cryptocurrencies.